


AI Security
Secure AI from development through runtime
CyberProof helps enterprises reduce risk across the AI lifecycle by bringing DevSecOps, governance, and runtime protection together in a managed service. Secure how AI applications and agents are built, governed, connected, and operated while continuously identifying, prioritizing, and reducing the exposures that matter most.
Three Pillars of AI Security

DevSecOps for AI
Embed security into AI development pipelines to find, prioritize, and remediate code and supply chain risk.

Governance for AI
Govern agent identity, access, tools, and behavior with least-privilege controls and runtime guardrails.

Protection of AI
Protect AI apps and APIs from abuse, bots, account takeover, malicious traffic, and sensitive data exposure.
AI Is Expanding Your Exposure
Traditional security was not built for AI systems
AI applications and agents combine code, models, APIs, identities, data, and autonomous workflows. Each layer can introduce vulnerabilities, excessive permissions, insecure dependencies, and new paths to sensitive systems that traditional controls may not fully address.
- AI-generated code and dependencies can introduce vulnerabilities and software supply chain risk before production.
- Agents and non-human identities can gain excessive permissions or operate beyond intended tasks and data boundaries.
- AI-facing applications and APIs can expose sensitive data or face bots, abuse, account takeover, and malicious traffic.
- Fragmented security controls make it harder to identify which exposures matter most and remediate them quickly.

What It Takes to Secure Agentic AI
Explore five short videos showing how enterprises can secure agentic AI across its lifecycle, from asset discovery and access control to monitoring, exposure management, and response to rogue behavior. See how visibility, guardrails, least privilege, continuous assessment, and remediation work together to reduce AI risk.
How leading enterprises are securing AI
Leading enterprises are treating AI security as a continuous lifecycle: discover the AI estate, govern agent access, protect sensitive data, monitor behavior and interactions, and maintain the auditability needed for governance and compliance. This creates a consistent foundation for scaling AI without losing visibility or control.
CyberProof AI Security Services
Managed security across the AI lifecycle
CyberProof brings together AI-focused DevSecOps, governance, runtime protection, and exposure management in a comprehensive managed service designed to reduce risk across the AI lifecycle.
- Secure AI development: Embed security into AI-augmented development with DevSecOps, code scanning, software supply chain controls, and remediation.
- Govern agent access: Define identities, least-privilege access, trusted tools, agent personas, and runtime guardrails for AI workflows.
- Protect applications and APIs: Discover and secure APIs, block malicious traffic, manage bots, and reduce account takeover and sensitive data exposure.
- Prioritize AI exposure: Connect vulnerability and exposure findings with threat context to focus remediation on the risks that matter most.
- Operate continuously: Combine managed security expertise, monitoring, validation, and continuous improvement as AI systems and threats evolve.

Business Outcomes from Secure AI Adoption
Scale AI with greater control, confidence, and resilience
- Accelerate secure AI adoption: Build security into development and runtime while enabling teams to move AI initiatives forward.
- Reduce AI exposure: Identify, prioritize, validate, and remediate code, identity, application, API, and infrastructure risks.
- Protect sensitive data: Control how agents and applications interact with enterprise data, APIs, tools, and services.
- Strengthen AI governance: Apply least privilege, runtime guardrails, trusted resources, and auditable controls across AI workflows.
- Improve operational resilience: Continuously monitor activity, reduce abuse, and adapt protection as AI systems and threats evolve.
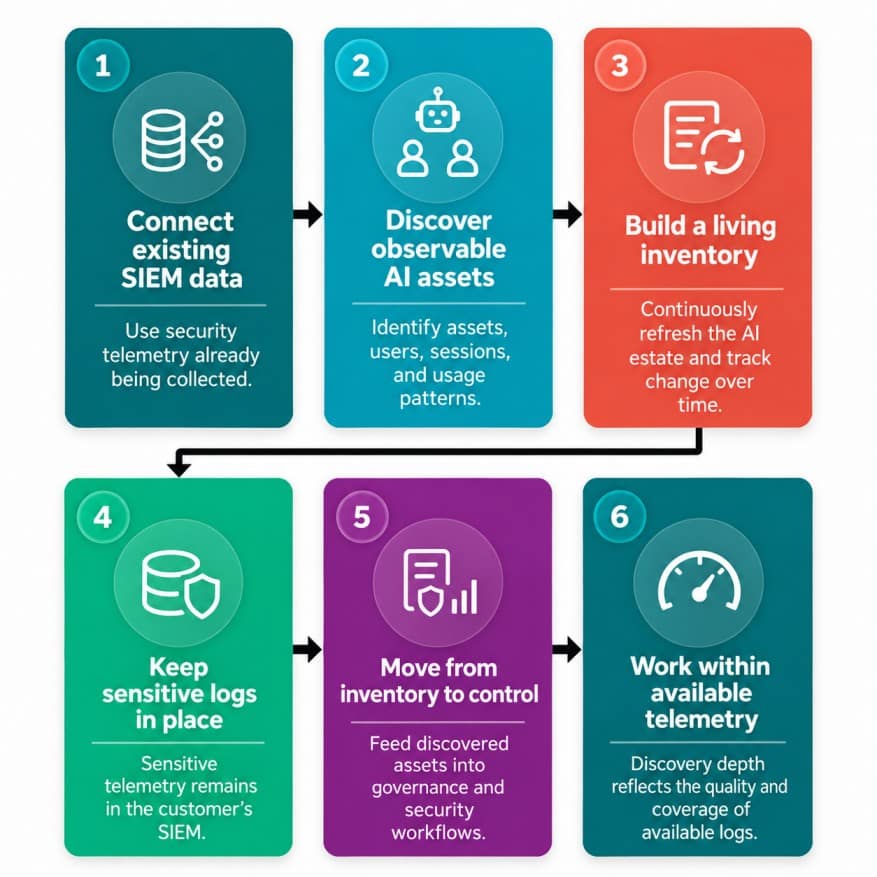
Discover What AI Is Really Running
Start with an AI Discovery Assessment
Get an evidence-based view of your AI estate, including observable agents, MCP servers, LLM providers, users, and usage patterns. Identify sanctioned versus unapproved activity, uncover governance gaps, and see where to prioritize access control, monitoring, and remediation.